Strong Passwords and Password Managers
What makes a password strong, why reusing one is dangerous, and how a password manager makes it easy.
A strong password is long, unique and hard to guess. The problem is remembering dozens of them, which is why password managers exist.
Why reused passwords are dangerous
Websites get breached all the time, and the stolen passwords are shared online. Attackers then try those same email and password pairs on other sites, like your email, bank and website admin. If you reuse a password, one breach unlocks everything.
What makes a password strong
- At least 14 characters long
- Different for every account
- Not based on names, birthdays or “Password123”
- A passphrase like
river-lamp-orange-42is strong and easy to type
Use a password manager
- It creates and stores a random password for every site
- You only remember one master password
- Good options include Bitwarden, 1Password and the built-in managers in Chrome or Apple devices
- Protect the manager itself with two-factor authentication
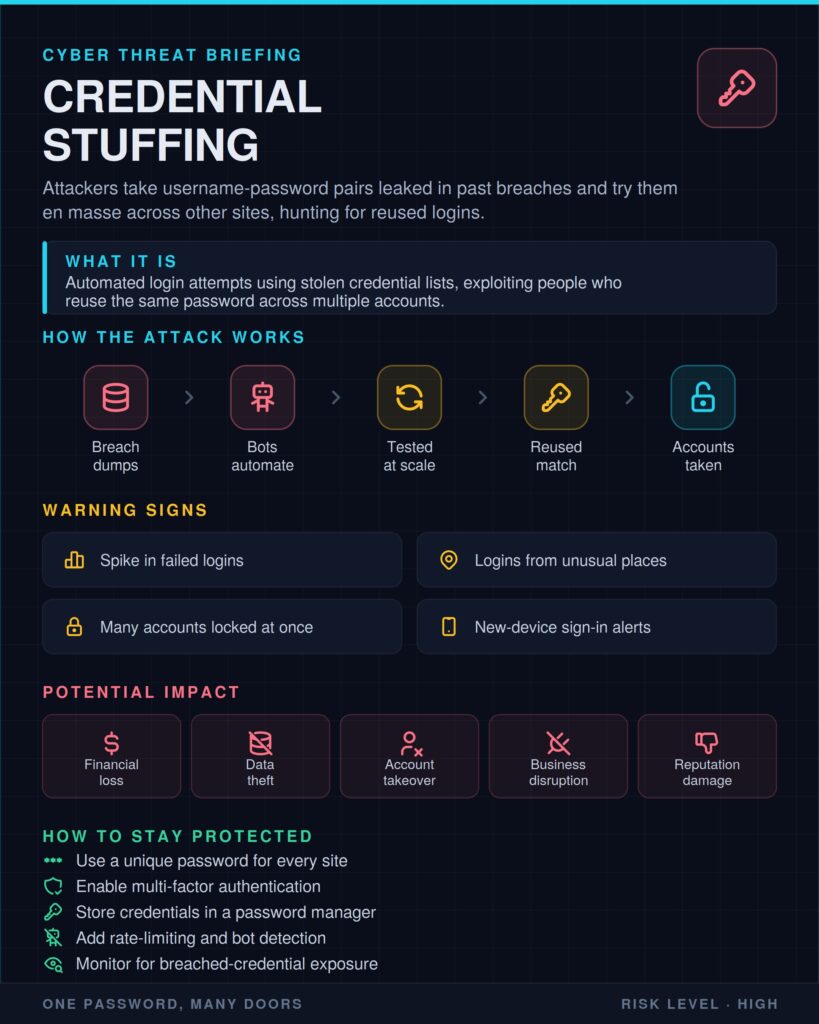
Use a different password for every account, and let a password manager remember them.