What is SQL Injection?
How a single login box can expose your whole database, and the simple coding fix that prevents it.
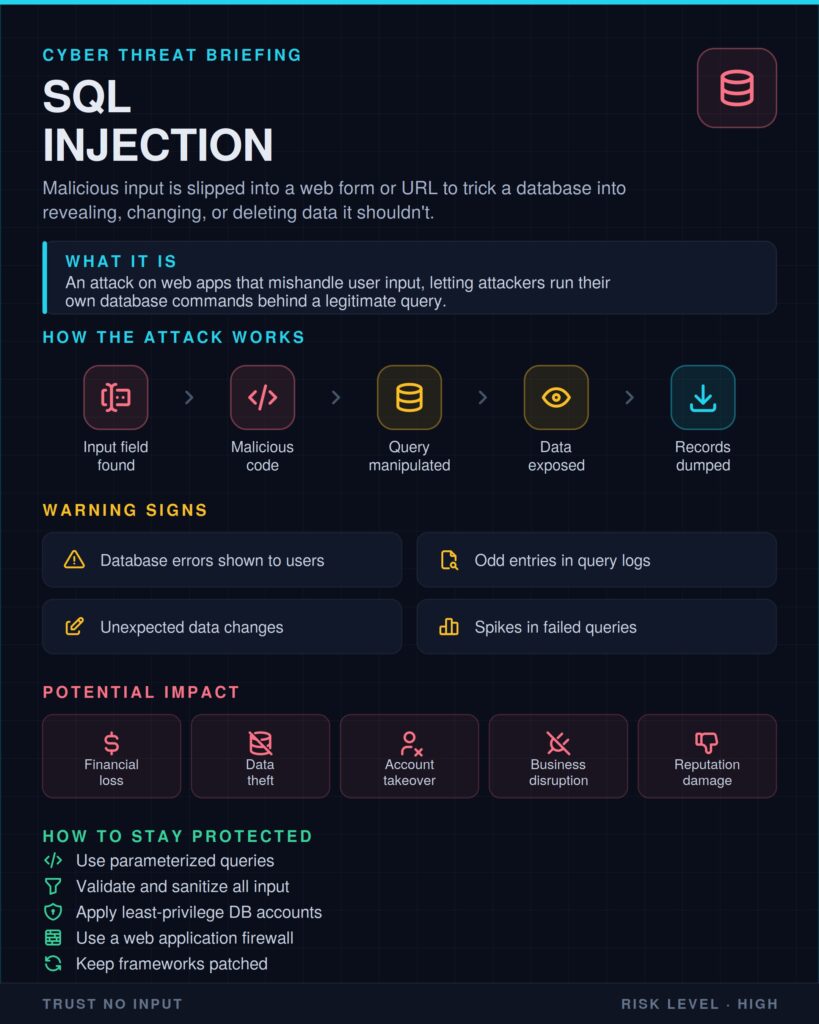
SQL injection is an attack where someone types database commands into a form on your site, such as a login or search box, and your database runs them.
How it works
Websites store data in databases and ask for it using a language called SQL. If the site builds those questions by gluing in whatever a user typed, an attacker can type SQL instead of a name. A classic example is typing ' OR 1=1 -- into a login box, which can trick a weak site into letting them in without a password.
What attackers can do
- Log in as any user, including admins
- Download customer names, emails and passwords
- Change or delete your data
- In bad cases, take over the whole server
How to protect your site
- Use prepared statements (parameterised queries) in all code
- Only install trusted, updated plugins
- Give the database user only the permissions it needs
- Add a web application firewall to block known attack patterns
Prepared statements stop almost all SQL injection. Ask your developer if your site uses them.